EU RED Cybersecurity Requirements Soon to Become Mandatory


The European Commission has adopted a delegated act under the Radio Equipment Directive (RED – 2014/53/EU), Delegated Regulation (EU) 2022/30, to strengthen the cybersecurity of internet-connected radio products in the European Union (EU). It applies from 1 August 2025.
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 1
 1.

Implementing three essential requirements of the RED
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 2

The delegated act activates three essential requirements in Article 3 of the Radio Equipment Directive, as follows:

  • 3(3)(d) Network protection: radio equipment must not harm the network or its functioning nor misuse network resources.

  • 3(3)(e) Protection of personal data and privacy: equipment must incorporate safeguards to protect the personal data and privacy of users and subscribers.

  • 3(3)(f) Protection from fraud: equipment must support features that ensure protection against fraud.
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 3

2

The EN 18031 series of harmonised standards

EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 4

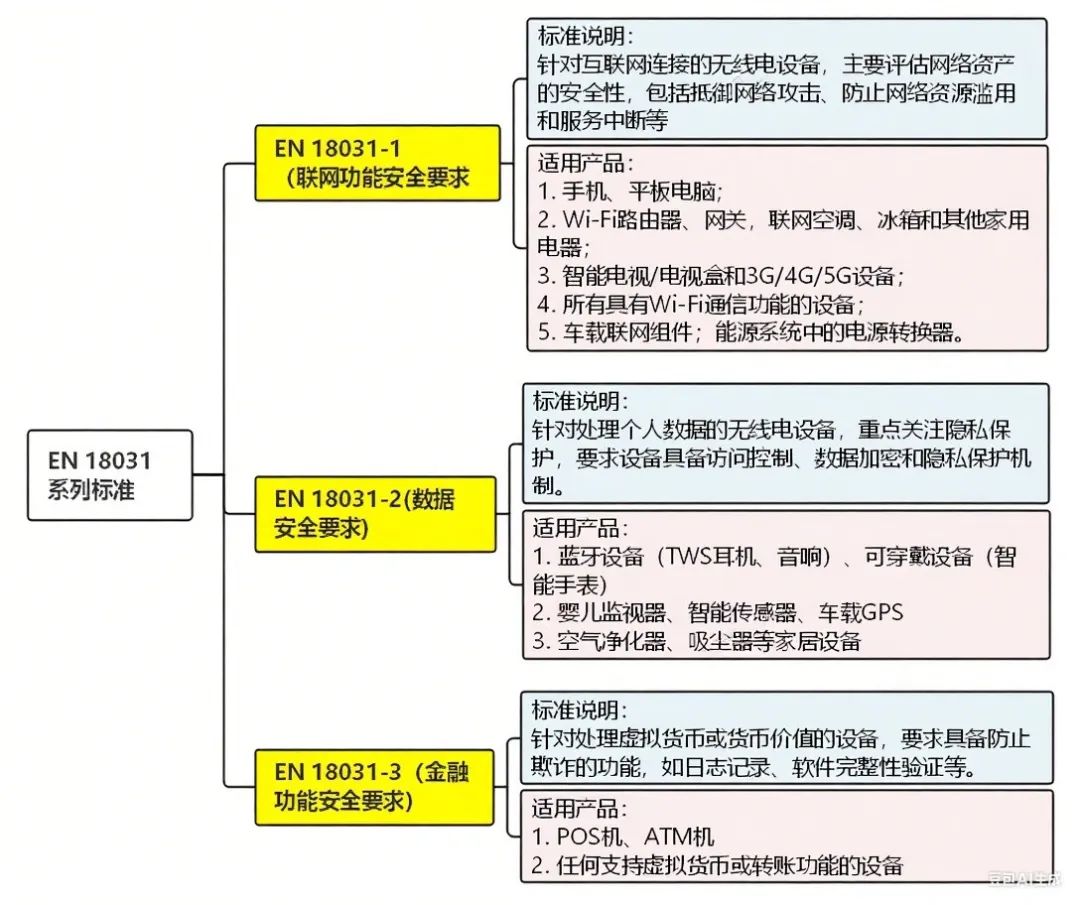
To meet these requirements, the European Commission has adopted the EN 18031 series as harmonised standards, each corresponding to one of the three RED requirements:

  • EN 18031-1: corresponds to 3(3)(d), focusing on network security requirements.

  • EN 18031-2: corresponds to 3(3)(e), covering personal privacy protection.

  • EN 18031-3: corresponds to 3(3)(f), focusing on protection against fraud.

3

Scope and assessment mechanism, in one chart:
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 5
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 6

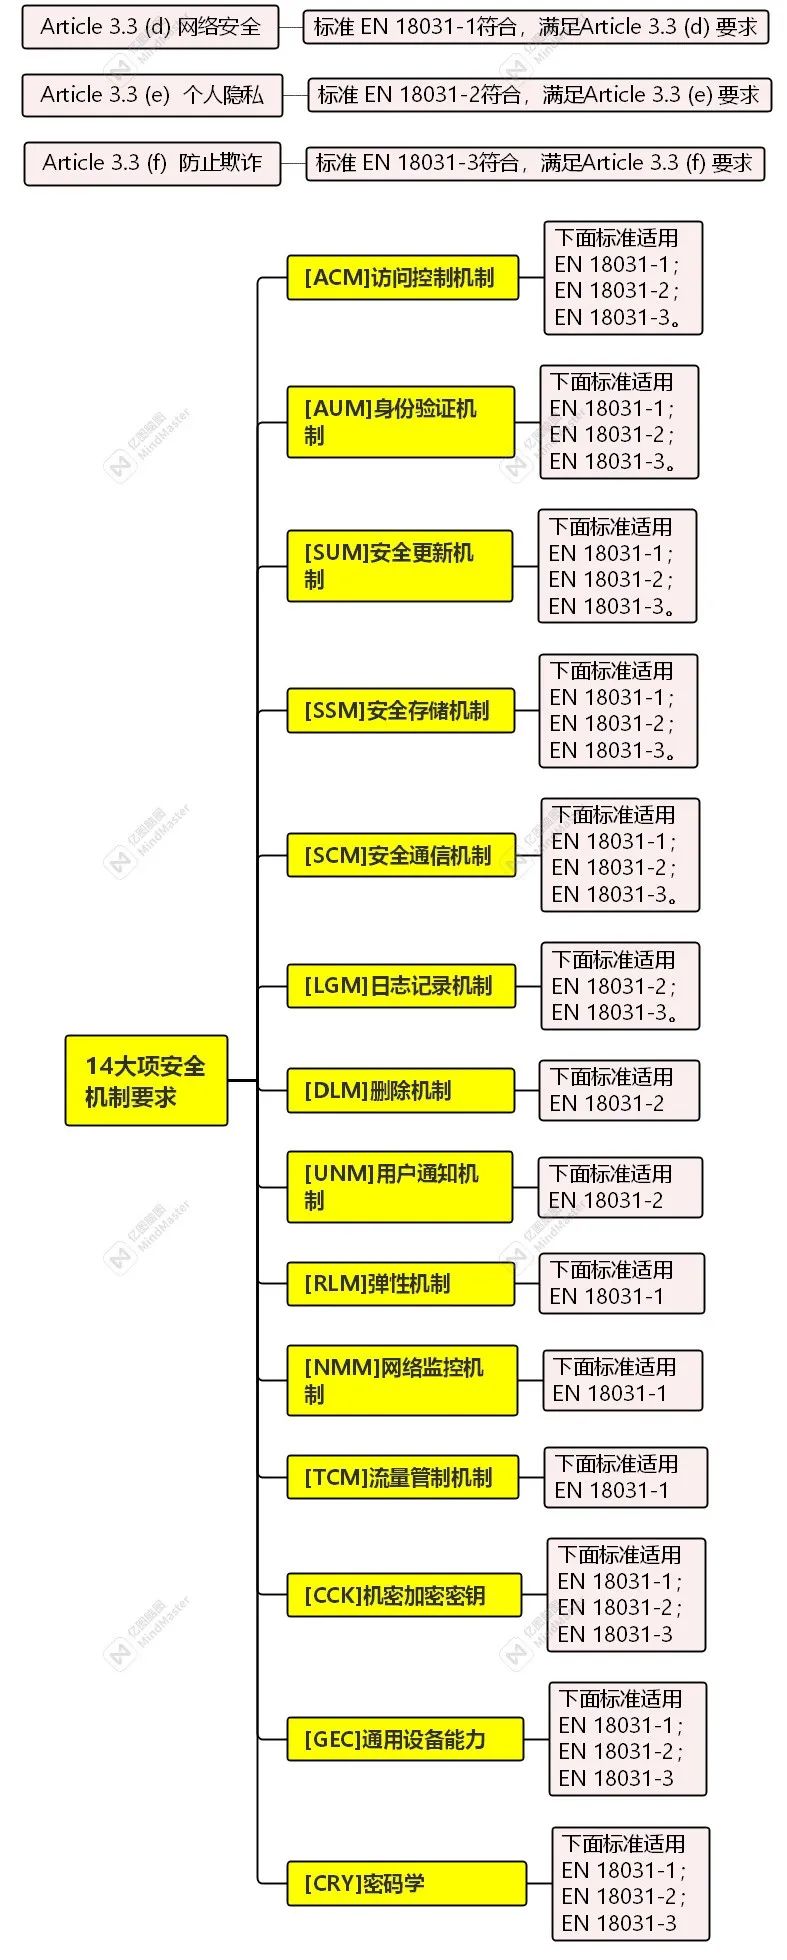
The EN 18031 series maps the assessment items to different security mechanism requirements (14 main items in total)
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 7
4

Recommendations for companies

EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 8

With just over a month left before the act applies, time is short. To avoid products being barred from the EU market after 1 August 2025 for not complying with the EN 18031 series, companies need to prepare the following test materials in advance:

  • Product samples and related software and apps;

  • Product instructions and user manuals;

  • Test application form;

  • Technical documentation (including the software bill of materials (SBOM), security design documents, etc.);

  • Questionnaire answers (as the basis for the decision trees);

  • Existing cybersecurity test reports (e.g. reports against ETSI EN 303 645 or IEC 62443-4-2).
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 9

END

Our services

EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 10
Everbiz has extensive hands-on experience in quality systems and product registration and can provide industry clients with professional consulting such as interpretation of the act and test guidance, helping companies meet regulatory challenges smoothly. If you have any questions, please contact us at any time.
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 11

More articles:

China NMPA Registration: Applying Real-World Data in Clinical Evaluation of Medical Devices

Detailed Guide to the Medical Device Classification Determination Procedure

The Complete Australian Medical Device Registration Process Explained

Clinical Evaluation Routes and Methods in MDR Certification

Guide to Writing MDR Technical Documentation

EU Safety Rules for Medical Device Apps on Online Platforms

EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 12

About Us

COMPANY INTRODUCTION
EVERBIZ Certification Services (Shanghai) Co., Ltd. (EVERBIZ) is a professional compliance service platform for testing, certification, consulting and training of medical products, dedicated to helping leading medical R&D companies at home and abroad improve their compliance capabilities and competitiveness. The company has offices and branches in Shanghai (China), Hong Kong, Munich (Germany), Salzburg (Austria) and Thailand, covering nearly 25 industries of compliance products (such as medical devices, new energy, household appliances, lighting, tools, laboratory instruments, machinery, in vitro diagnostics, wireless products and reagents).
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 13

Our Offices

COMPANY  ADDRESS
Shanghai: Room 705, Building 6, Lane 111, Luxiang Road, Baoshan District, Shanghai | Germany: Landsberger Str. 155, 80687 München, Germany
Austria: Innsbrucker Bundesstraße 136/3, 5020 Salzburg, Austria
Hong Kong: Room A1, 11/F Winner Building, 36 Man Yue Street, Hung Hom, Kowloon, Hong Kong
Thailand: No. 850 Soi Lat Krabang 30/5, Lat Krabang Subdistrict, Bangkok 10520
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 14
EU RED Cybersecurity Requirements Soon to Become Mandatory – Figure 15


Scroll to Top